
AI is already inside the nonprofit, but only 4 percent of surveyed nonprofits had documented, repeatable workflows. The governance question is whether mission, data, human judgment, and community trust are still in charge.
Nonprofits rarely adopt AI through one board-approved decision. It usually arrives one task at a time.
A development officer drafts a grant proposal with AI. A donor platform adds automated segmentation. A program manager summarizes client notes. A vendor offers a free pilot to prioritize service requests.
Each decision looks modest. Together, they determine whose data can be used, which errors are acceptable, when a human must intervene, and who bears responsibility when an automated recommendation affects a person. By the time leadership asks whether the organization is using AI, the answer is often already yes. The governance question is whether that use is accountable or still a collection of individual experiments.
The Gap Is Not Adoption. It Is Organizational Readiness.
That distinction is visible in the 2026 Nonprofit AI Adoption Report. In its survey of 346 nonprofit organizations, 92 percent reported using AI in some capacity. Yet only 4 percent had documented, repeatable AI workflows.
Only 4 percent is not a footnote. It is a governance warning. It tells us that access to AI has moved much faster than the shared rules, evidence, and decision rights needed to use it consistently.
The same benchmark found that 81 percent were using AI individually and ad hoc, nearly half had no AI governance policy, and only 7 percent reported major mission-level improvements. The survey focused on fundraising and operations, not the entire sector. Still, it captures a pattern many organizations will recognize: adoption has outpaced institutional readiness.
As James A. Lomastro argues in Nonprofit Quarterly’s examination of AI governance, nonprofits must decide whether they will help shape how AI is funded, constrained, and used or leave those choices to more powerful actors.
Mission-driven status does not make technology mission-aligned. Good intentions do not prevent unreliable outputs, privacy failures, biased outcomes, weak contracts, or mission drift. Many nonprofits serve people with limited power to refuse data collection, challenge a recommendation, or recover from an error. Community trust is an operating asset.
In my whitepaper, Responsible AI, Explained, I distinguish responsible AI from the architecture that makes it operational. Responsible AI supplies the substantive commitments. AI governance determines who approves a use, owns the risk, evaluates vendors, retains evidence, and decides when an application must be paused or withdrawn.
Nonprofits do not need a Fortune 100 compliance bureaucracy. They need a right-sized governance model that can answer four questions: What AI are we using? What is the risk? What controls apply? Where is the evidence?
Here are seven ways to build one.
1. Start With the Mission Outcome, Not the Instrument
The first question should not be, “Where can we use AI?” It should be, “What human or organizational problem are we trying to solve?” This is the core of a human-in-the-loop approach.
An AI assistant that drafts donor communications does not present the same risk as an application that ranks people for housing, health, employment, education, or legal assistance. The architecture may be similar. The consequences are not.
Leadership should define the mission benefit, affected people, evidence of success, and unacceptable harm before selecting a platform. This reflects the first of Anant’s 8 Principles for Getting AI Nativity Right: begin with the human outcome and organizational need. Technology follows. Sometimes the responsible decision is a limited pilot, a redesigned process, or no AI at all.
| Executive question: What mission outcome justifies this use, and what consequence would make us stop? |
2. Give AI a Governance Home
AI cannot belong solely to IT, an enthusiastic employee, or a vendor. The board should oversee mission alignment, risk appetite, and consequential uses. Management should name an accountable executive and a cross-functional forum with authority to approve, condition, pause, or reject AI uses.
Relevant perspectives may include program leadership, legal, privacy, cybersecurity, data, fundraising, human resources, communications, and frontline staff. When AI affects beneficiaries or communities, people with lived experience should have a meaningful role. This may fit within an existing committee. What matters is clear ownership and real decision rights.
| Executive question: Who can authorize this use, require safeguards, and stop it when the risk changes? |
3. Inventory AI and Classify Uses by Risk
An organization cannot govern AI it cannot see. The inventory should capture standalone platforms, AI embedded in existing software, vendor-operated applications, informal employee use, datasets, owners, affected populations, data types, intended outputs, and approval status.
Then classify the use case, not merely the product. Distinguish prohibited, restricted or high-impact, approved-with-controls, and low-risk uses. Risk should reflect consequences for people, data sensitivity, autonomy, scale, reversibility, and legal exposure. As I explained in From Agent to Action, organizations should not give an AI agent power they cannot trace, contain, or unwind.
| Executive question: Do we know every AI use in the organization and the risk tier assigned to it? |
4. Create an Enabling Policy With Clear Red Lines
A useful policy tells employees what is encouraged, what requires approval, and what is prohibited. A vague instruction to “use AI responsibly” transfers institutional risk to individual employees. A blanket ban often drives the same activity underground.
The policy should address approved environments, sensitive data, verification, disclosure, copyright, records, privilege, and human review. Red lines might include client information in unapproved public applications, final eligibility decisions made by AI, professional advice without qualified review, or autonomous changes to records or funds. High-impact uses should trigger an impact assessment, privacy and security review, testing, and approval.
| Executive question: Can an employee tell, without guessing, what is allowed, restricted, and prohibited? |
5. Design With Affected People, Not Merely for Them
An application can improve an aggregate metric and still undermine autonomy, dignity, or trust. In the fictional Princeton Automated Healthcare App case study, developers improved performance for underrepresented groups, but criticism followed when users learned about curated content, risk classifications, and experimentation without meaningful consent.
Statistical improvement does not resolve every ethical question. When AI affects people, nonprofits should provide plain-language notice, seek meaningful consent where appropriate, test for uneven outcomes, and offer accessible correction, appeal, and redress. Participation must be capable of changing the decision, not merely validating an architecture already chosen.
| Executive question: Have the people who will bear the consequences had a meaningful voice in the design and review? |
6. Govern Vendors, Funders, and “Free” AI
Free technology is rarely free. A nonprofit may pay through data access, vendor dependence, reputational exposure, or the gradual transfer of influence over mission priorities.
The fictional Princeton Public Sector Data Analytics case study shows how a pro bono project can expand beyond its original purpose while the provider gains data, experience, and commercial advantage. Donated and grant-funded AI deserves the same diligence as purchased technology. Review data use, retention, training, security, subprocessors, accessibility, audit rights, incident notice, model changes, portability, and exit rights. Require renewed approval when a pilot moves from analysis into ranking people, allocating services, or taking action.
| Executive question: What is the organization giving up in exchange for the technology, and can it exit safely? |
7. Keep Humans, Evidence, and Stop Mechanisms in the Architecture
Human review is meaningful only when the reviewer has the information, competence, time, and authority to disagree with the AI. A person who clicks “approve” under workload pressure is not an accountability layer.
Before deployment, test accuracy, bias, security, hallucination, accessibility, and foreseeable failures in the organization’s context. After deployment, monitor complaints, overrides, uneven outcomes, vendor changes, policy violations, and mission benefit. Define an AI incident, notification and evidence duties, and when the use must be paused or rolled back.
As explored in When AI Becomes Evidence, Who Is Culpable?, governance decisions and system records may later become evidence in an investigation, dispute, or public accountability process. If an organization cannot reconstruct what the AI did and who had authority to intervene, it does not have meaningful accountability.
| Executive question: Can we reconstruct the decision, identify the accountable human, and stop the application before harm compounds? |
From Experimentation to Institutional Capability
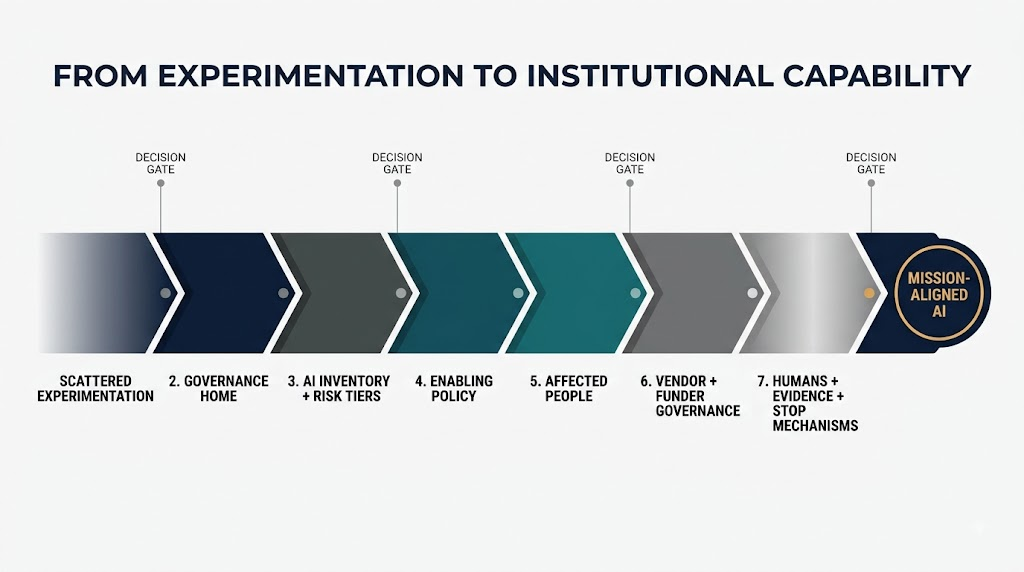
The 4 percent finding is not a reason for nonprofits to retreat from AI. It is a reason to become more deliberate about the transition from individual experimentation to institutional capability.
At the next executive or board meeting, ask four questions: What AI are we using? Who owns it? Which uses could affect people, mission, or sensitive data? What evidence shows they were reviewed, tested, and approved?
The answers will reveal where governance is missing. Name an accountable executive, complete an initial inventory, identify the highest-risk uses, and establish the rules that apply before those uses expand. The voluntary NIST AI Risk Management Framework offers a useful structure, but a framework creates value only when it becomes authority, controls, documentation, and decisions.
The goal is not to make AI impossible. It is to make its use explainable, defensible, participatory, and aligned with mission.
Responsible AI is not a policy document added after adoption. It is the discipline that allows a nonprofit to use powerful technology without outsourcing its judgment, compromising its purpose, or asking the communities it serves to bear risks they never agreed to accept.
Read More From Anant
- 8 Principles for Getting AI Nativity Right
- From Agent to Action: Navigating the Agentic AI Liability Gap in Critical Infrastructure
- When AI Becomes Evidence, Who Is Culpable?
About Lili Kazemi
Lili Kazemi is General Counsel and AI Policy Leader at Anant Corporation, where she advises on AI governance, risk, compliance, contracts, and policy. She brings more than 20 years of experience across Big Law, Big Four, and federal government roles, with a background in international tax, regulatory strategy, and cross-border legal frameworks. She is completing her certification the London School of Economics and Political Science’s Ethics of AI Masterclass and writes The Human Edge of AI, a LinkedIn newsletter examining AI at the intersection of law, policy, work, and everyday life.
You can now also follow Lili on substack at https://substack.com/@lilikazemi
Subscribe – The Human Edge of AI
About Anant
Anant helps forward-thinking teams unlock the power of AI safely, strategically, and at scale. From legal and policy to data, knowledge, security, and enterprise architecture, Anant helps organizations build workflows that act, automate, and aggregate without losing human judgment or accountability.
Disclaimer
This article is provided for general informational purposes and does not constitute legal advice. It reflects the author’s independent analysis and should not be treated as an endorsement by any organization cited.